The Problem With Traditional Antivirus
Traditional AV relies on signature matching — comparing files against a database of known threats. It works well against yesterday's malware. It fails against:
- Fileless attacks using PowerShell, WMI, and other trusted OS tools
- Polymorphic malware that rewrites its own code to evade detection
- Zero-day exploits with no existing signature
- AI-generated payloads built specifically to bypass known detection patterns
Nearly 54% of organizations report difficulty detecting fileless attacks — because antivirus treats these tools as "authorized" and lets them run.
Why EDR Changes the Game
🕵️ Behavioral Detection, Not Just Signatures
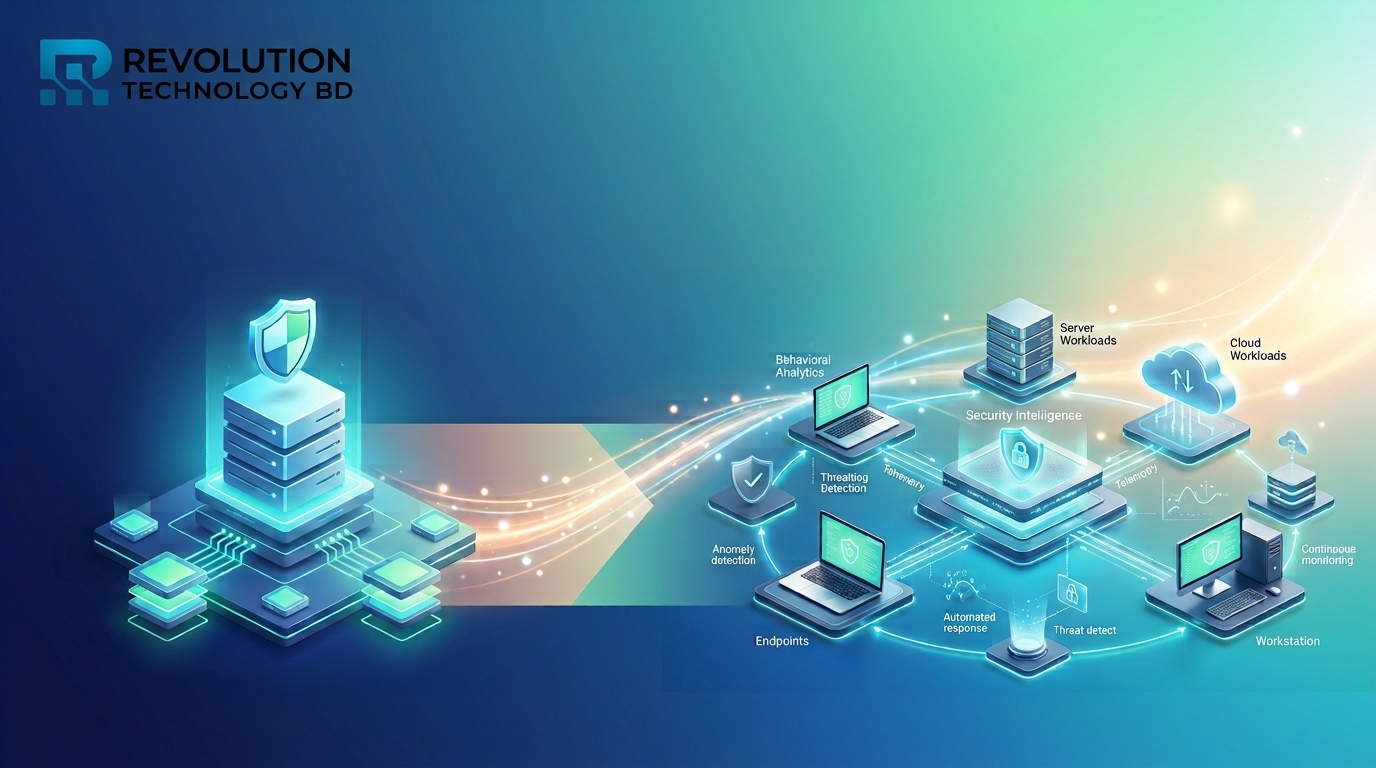
EDR monitors how processes behave, not just what files look like. Ransomware encrypting hundreds of files in seconds gets flagged instantly — even if it's never been seen before.
⏱️ Real-Time Response
Continuous monitoring + automated isolation means a compromised device can be quarantined in seconds, not hours — cutting off lateral movement before it spreads.
🧩 Full Visibility
One dashboard shows every endpoint, every alert, every action taken — across the entire organization.
🛡️ Compliance-Ready
Auditable detection-and-response logs are now expected by regulators and cyber insurance providers — plain AV can't produce this.
Next-Gen Endpoint Security: 4 Key Capabilities
01 — AI-Driven Behavioral Analytics
Detects malicious patterns, not just known malware signatures.
02 — Fileless Attack Detection
Flags misuse of legitimate tools (PowerShell, WMI) used in living-off-the-land attacks.
03 — Automated Response
Auto-isolates infected devices, kills malicious processes, rolls back damage — no manual delay.
04 — XDR Integration
Correlates endpoint + network + email + cloud data for full attack-path visibility.
Who Needs This Most?
Corporate Offices • Banks & Financial Institutions • Hospitals • Manufacturing/OT Environments • Educational Institutions • Retail & POS Systems
Is Your Business Protected?
Ask yourself:
- How many endpoints are actually monitored — not just "installed with AV"?
- Can your current solution detect fileless/behavioral threats?
- If a device is compromised right now, how fast can you isolate it?
- Do you meet compliance/insurance requirements for documented incident response?
Revolution Technology BD brings enterprise-grade EDR solutions — SentinelOne, Sophos, Kaspersky, Trend Micro, Microsoft Defender — to help you close the gap legacy antivirus leaves open.
For more info visit: Endpoint security Solution
Antivirus blocks what it recognizes. EDR catches what it doesn't. In 2026, that difference decides whether an attack gets stopped in seconds — or spreads for days.
Protect Your Endpoints. Build a Smarter Security Future.
Revolution Technology BD — Technology for Today. Solutions for Tomorrow.